Replace Legacy VPN With Zero Trust for SaaS and On-Premises Apps

Modernize remote access for work-from-home employees and contractors with identity- and device-aware, least-privilege access to SaaS and on-premises applications through one ZTNA gateway
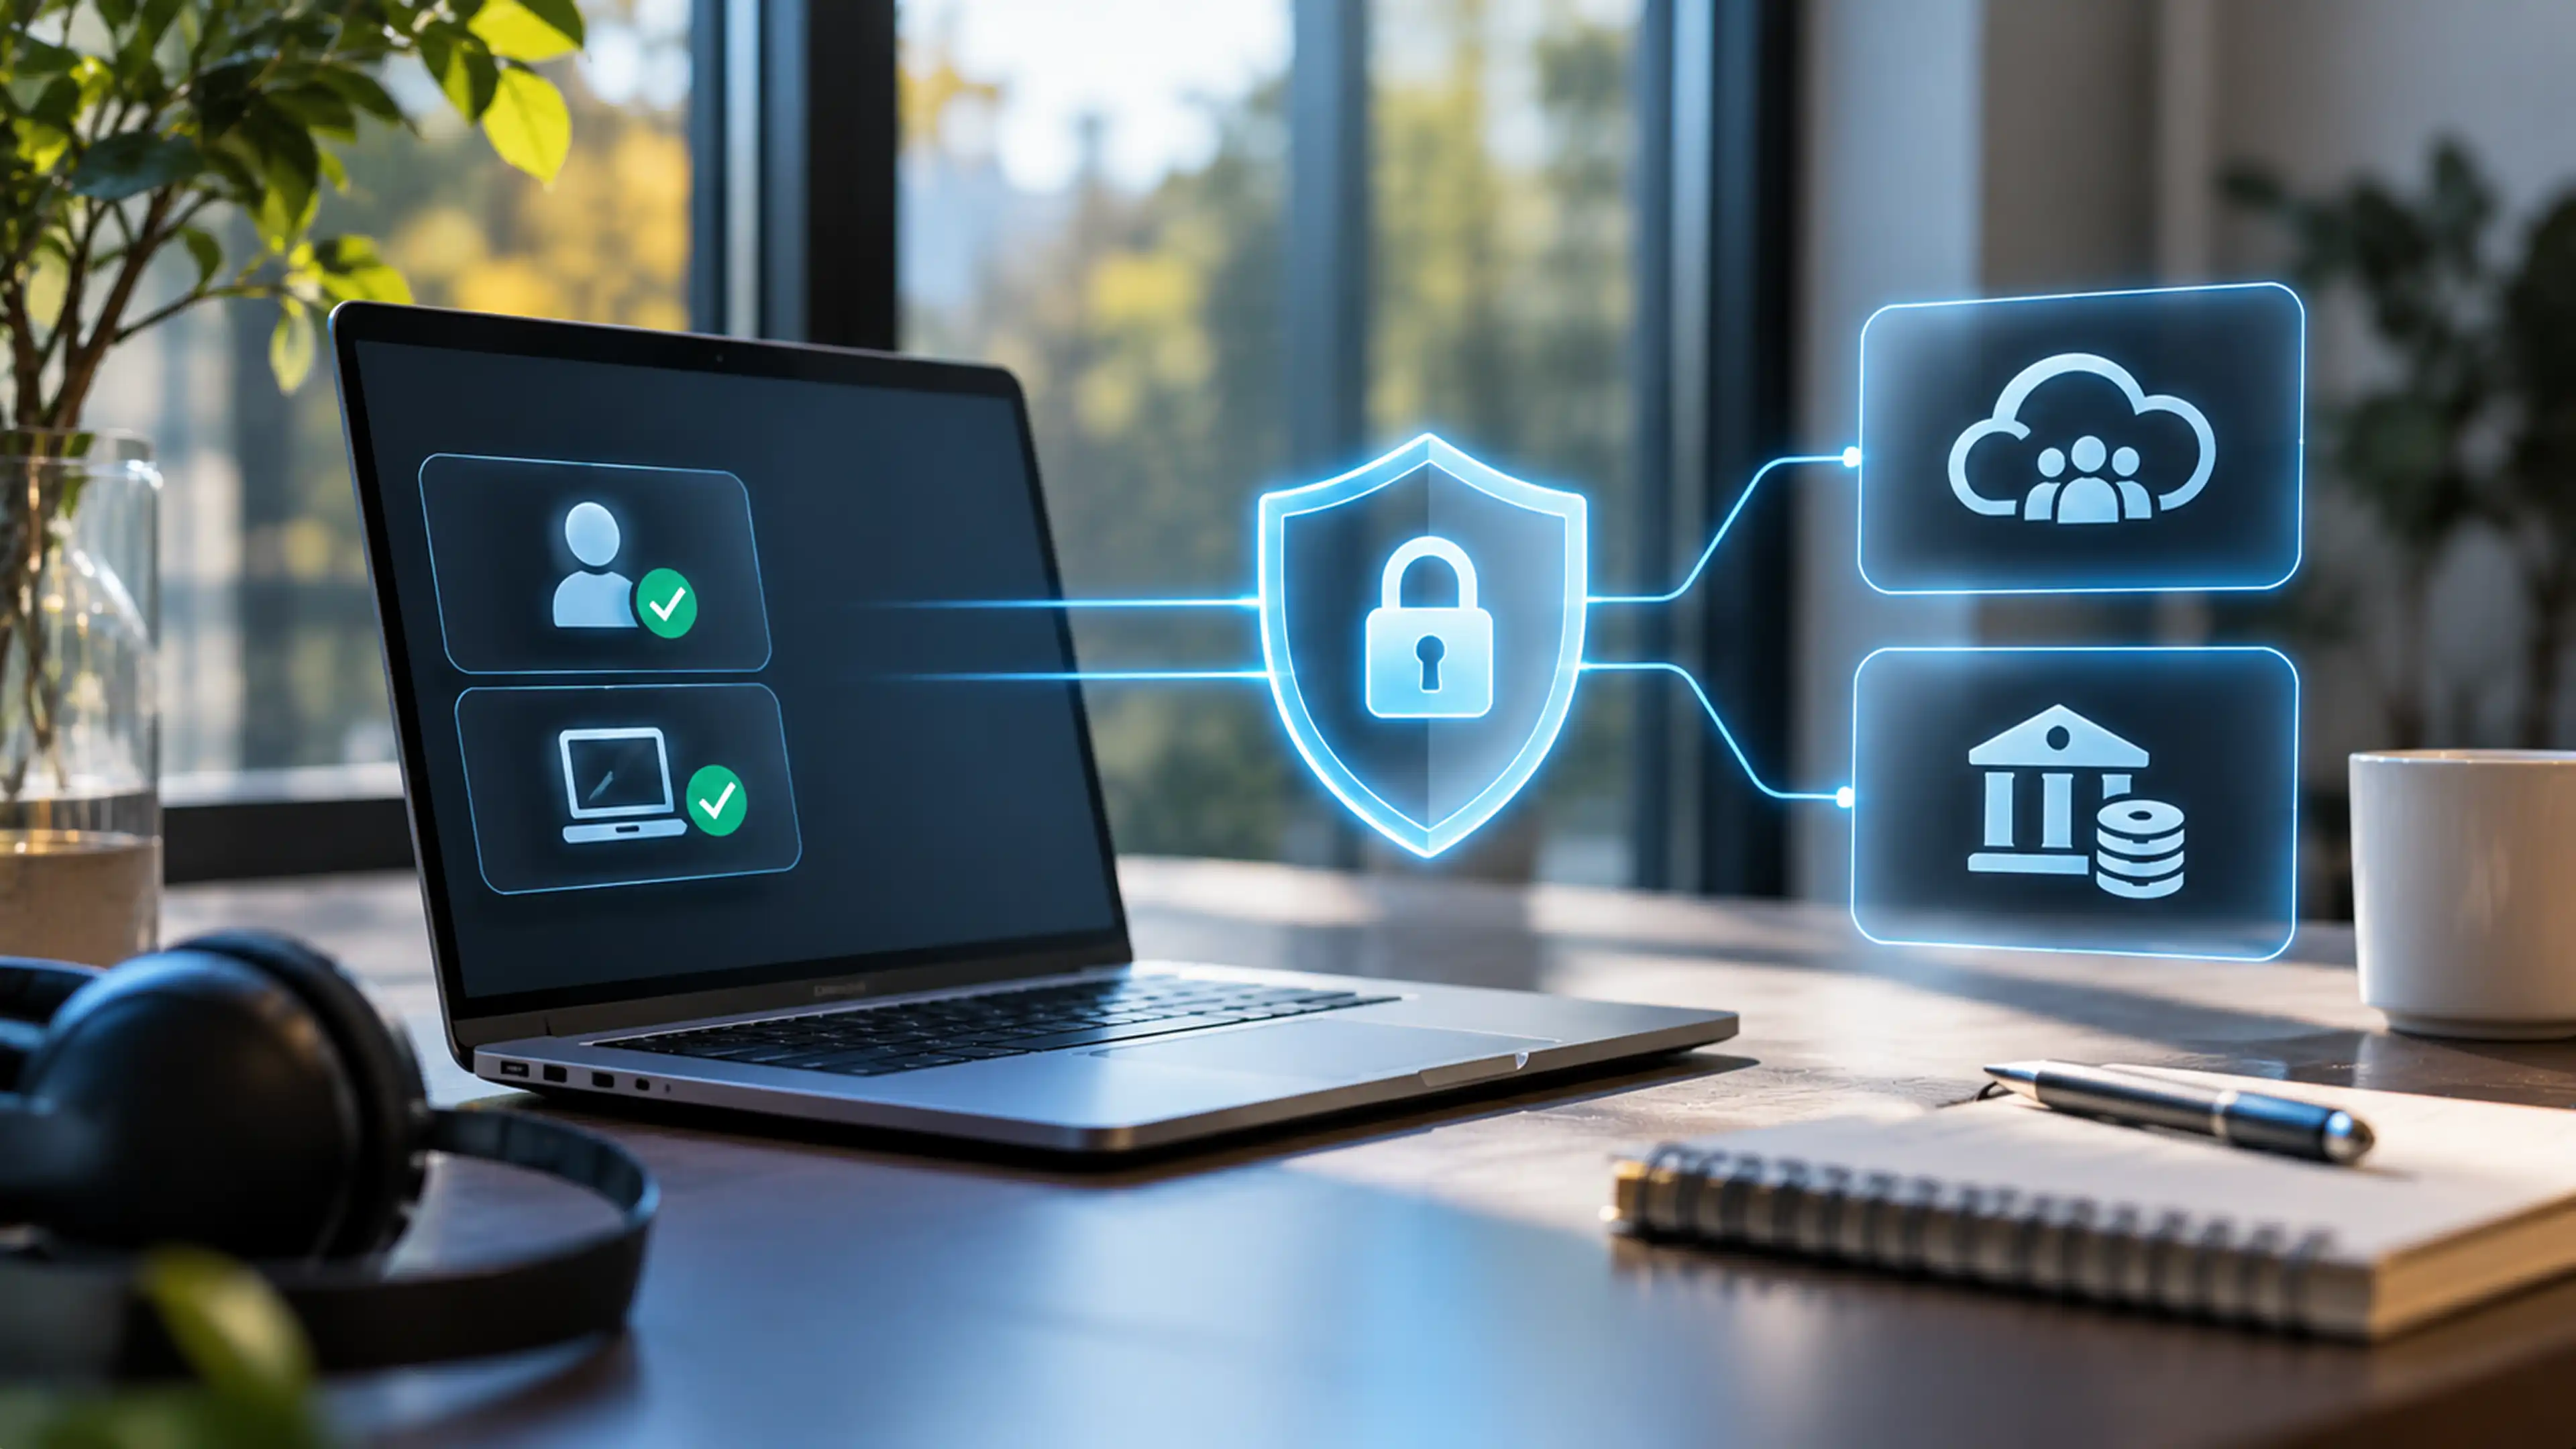
Zero Trust application access replacing traditional network VPN connections
Challenges

Network-wide trust is no longer sufficient

Traditional VPNs connect work-from-home employees and remote contractors to a network, not to individual applications under a unified identity policy. They can expose more internal resources than a user needs, increasing lateral-movement risk. VPNs also cannot control access to cloud-hosted SaaS applications, leaving a major security gap even when private-network access is protected
SaaS control gaps
Traditional VPNs do not enforce application-level authorization for SaaS access
Broad network exposure
VPN access can expose more network resources than users need
Diverse remote workers
Employees and contractors require different application permissions
Capabilities

How Zaperon replaces legacy VPN access

Four connected security controls bring visibility, authorization, enforcement and auditability together.
Give least-privilege access to SaaS applications
Integrate any SaaS application with Zaperon and assign user-specific permissions—coverage that legacy VPNs cannot provide
Control on-premises access without broad network trust
Permit only explicitly assigned internal applications and infrastructure through the Zero Trust gateway
Verify identity and device posture continuously
Replace password-centric access with PKI certificates, Zaperon Verify MFA and contextual device checks
Use one policy gateway for hybrid application estates
Apply consistent access controls to SaaS and on- premises applications for work-from-home employees and remote contractors
How It Works

Replace Network Trust With App-Specific Access

01
Inventory SaaS and on-premises applications used by work-from-home staff and remote contractors
02
Integrate applications with Zaperon and assign user-level permissions
03
Configure PKI passwordless authentication, device posture and role-based access policies
04
Move access to the Zero Trust gateway and phase out broad VPN-based network permissions
Real-World Scenario

A hybrid employee accesses SaaS and on-premises apps

A contractor working remotely needs a cloud CRM and one internal finance portal. A VPN can connect the contractor to a company network but does not control their SaaS CRM access. Zaperon integrates both applications, grants least-privilege access under the contractor’s identity and device policies, and avoids broad network connectivity

01
Validate: Verify identity and device posture before access.
02
Authorize: Grant least-privilege SaaS and on-premises application access
03
Protect: Avoid granting broad network-level trust
Business Outcomes

Reduce Attack Surface Without Slowing Remote Work

Enable secure BYOD access for assigned employees and contractors across desktops and mobile devices
Enforce application-by-application BYOD permission and desktop/mobile access policies
Reduce data exfiltration risk while isolating enterprise data from users’ personal information
What's New

Related Insights & Resources

Frequently Asked Questions

Still have a questions?
Can't find the answer to your question? Send us an email and we'll get back to you as soon as possible.

Request a Demo

Can VPNs secure SaaS application access?
No. A conventional VPN establishes a network connection and does not enforce user-level authorization for internet-hosted SaaS applications. Zaperon integrates SaaS applications and applies least-privilege access policies to each user.
Does replacing VPN also secure on-premises applications?
Yes. Zaperon uses a unified Zero Trust Access gateway to enforce user- and device-aware access to both SaaS and on-premises applications, including for work-from-home employees and remote contractors.

Take Control of Your
Security in the AI Era

Book a Demo