Stop Sensitive Data Leaks at the Point of Risk

Protect structured and unstructured enterprise information with consistent identity-aware DLP across endpoints, email, SaaS and AI on Windows, Linux and Mac
Protection of confidential enterprise data across applications and communication channels
Challenges

Sensitive data moves across more channels than ever

Confidential information can leave through an endpoint, email, a SaaS application or an AI interaction. It can be a structured record or an unstructured file such as source code, a drawing or a business document. Different security policies for each channel or operating system create avoidable gaps
Unstructured information
Source code, designs and intellectual property cannot be protected by simple keywords alone
Disconnected channels
Endpoints, email, SaaS and AI require consistent DLP enforcement
High-risk transfers
Sensitive data can be copied or sent to unauthorized destinations
Capabilities

How Zaperon stops sensitive data leakage

Four connected security controls bring visibility, authorization, enforcement and auditability together.
Detect structured and unstructured content
Identify PII, PHI, payment data, intellectual property, source code and sensitive information in multiple file types
Enforce DLP consistently across channels
Apply the same DLP policies across endpoints, email, SaaS applications and AI workflows on Windows, Linux and Mac
Use identity-aware context
Evaluate user identity, role, device trust, data sensitivity and the intended destination before allowing movement
Stop unauthorized data disclosure
Inspect content and block policy-violating transfers before sensitive data leaves an approved boundary
How It Works

Detect Sensitive Data and Enforce DLP in Real Time

01
Define sensitive data patterns, unstructured content categories and authorized destinations
02
Apply the same protection policy across endpoints, email, SaaS and AI on Windows, Linux and Mac
03
Inspect content in multiple file types and enforce allow/block decisions
04
Analyze policy events, adapt exceptions and use audit records for governance
Real-World Scenario

An employee tries to share a confidential file

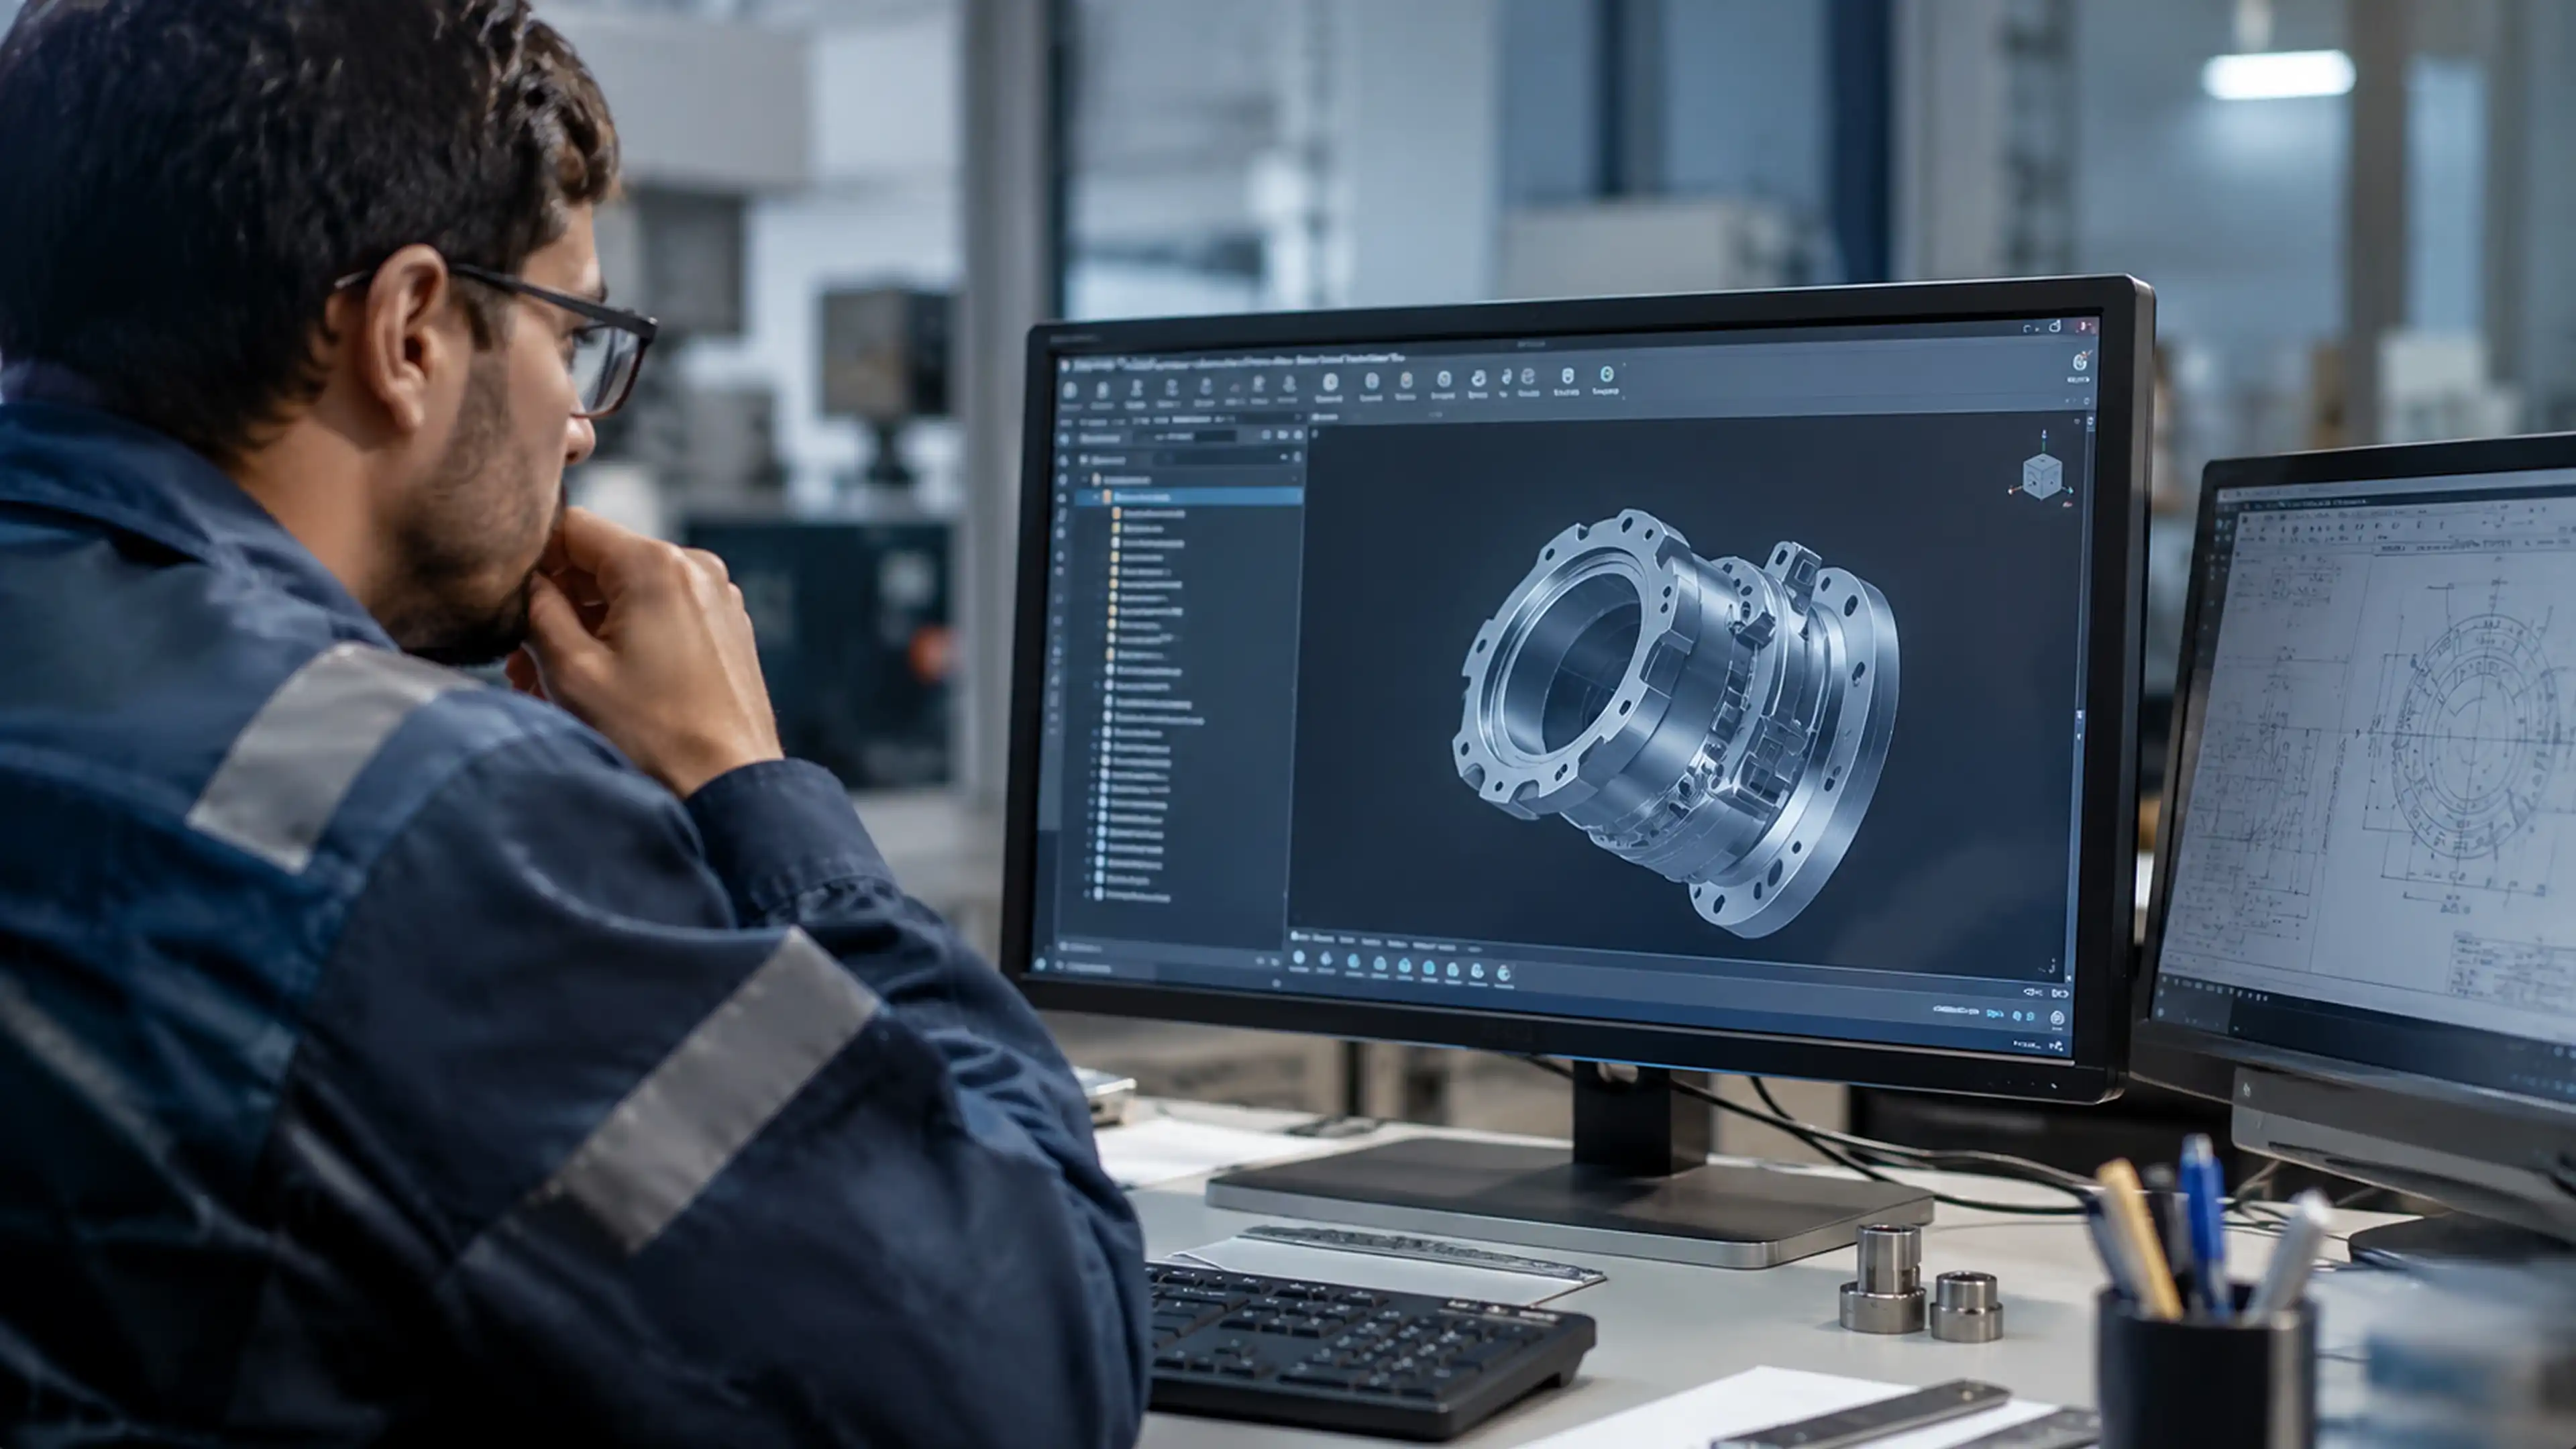
A manufacturing engineer tries to send a CAD drawing through email and later submits an extract to an AI tool. Zaperon applies the same DLP controls across both channels and blocks transfers that violate the organization’s policy

01
Classify: Detect confidential structured and unstructured files
02
Enforce: Apply the same DLP policies across endpoint, email, SaaS and AI
03
Audit: Record blocked transfers and review security events
Business Outcomes

Keep Confidential Data Within Approved Channels

Enable secure BYOD access for assigned employees and contractors across desktops and mobile devices
Enforce application-by-application BYOD permission and desktop/mobile access policies
Reduce data exfiltration risk while isolating enterprise data from users’ personal information
What's New

Related Insights & Resources

Frequently Asked Questions

Still have a questions?
Can't find the answer to your question? Send us an email and we'll get back to you as soon as possible.

Request a Demo

Can Zaperon inspect unstructured information and different file types?
Yes. Zaperon inspects structured and unstructured data across multiple file types, including sensitive documents, source code and engineering information, under administrator-defined DLP policies
Is DLP consistent across Windows, Linux and Mac?
Yes. Zaperon applies the same DLP capabilities across endpoints, email, SaaS and AI on Windows, Linux and Mac

Take Control of Your
Security in the AI Era

Book a Demo