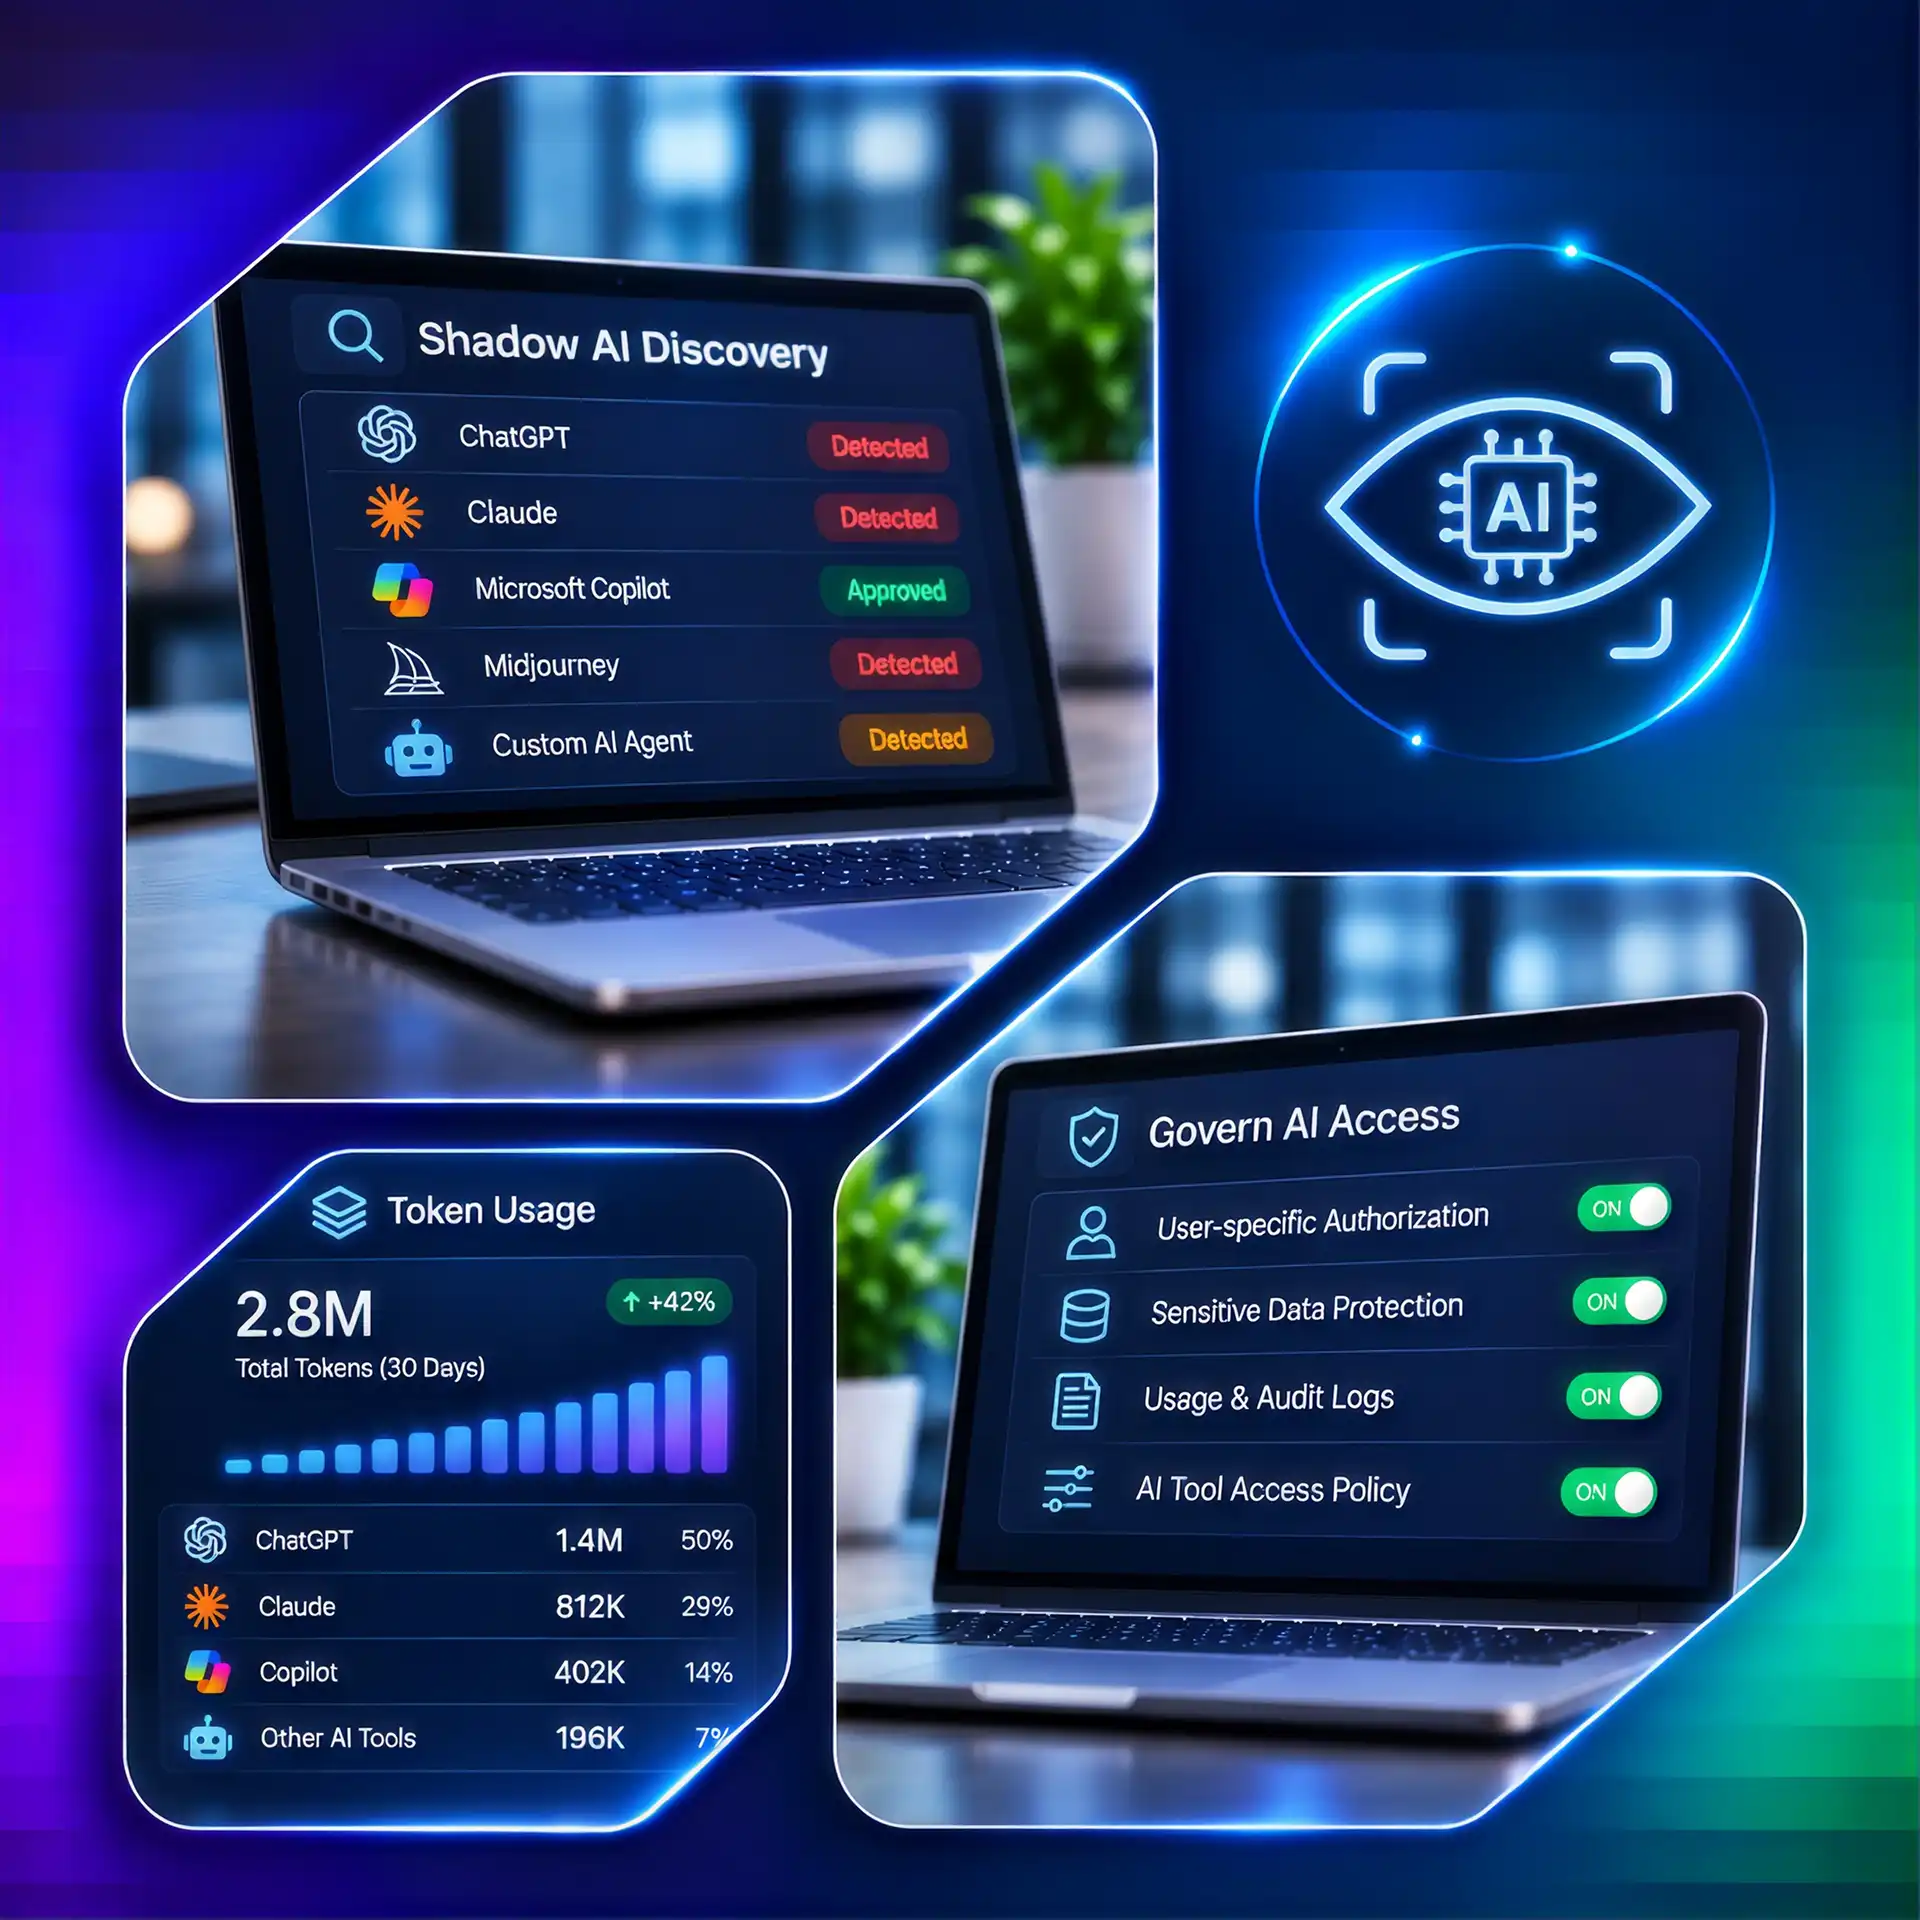
Discover Shadow AI Across Your Enterprise. Govern It With Confidence

Discover public GenAI tools, SaaS copilots and employee-developed AI agents, connect their activity to users and devices, and govern access and sensitive data with Zaperon
Discovery and governance of unsanctioned AI applications used across an enterprise
Challenges

AI adoption moves faster than security reviews

AI adoption often starts before a formal IT review. Employees use public GenAI, embedded SaaS copilots and custom agents created with tools such as Microsoft Copilot or n8n. Without discovery, security teams cannot consistently identify which tools are in use, who is accessing them or what enterprise information is being shared
Unseen AI tools
Public GenAI tools and SaaS copilots emerge outside formal IT reviews
Unknown agent ownership
Employee-created workflows may connect to business applications without oversight
Uncontrolled data flows
Prompts, uploads and agent exchanges can expose sensitive enterprise data
Capabilities

How Zaperon closes the Shadow AI gap

Four connected security controls bring visibility, authorization, enforcement and auditability together.
Discover diverse AI usage
Identify public GenAI services, SaaS copilots and self-developed agents in use across the workforce, including employee-launched workflows
Attribute AI usage to people and devices
Correlate AI activity with user identity, role and device context across endpoints, SaaS and cloud environments
Control sanctioned and unsanctioned AI
Apply identity-aware authorization policies to permit approved tools and restrict risky or unapproved AI access
Protect data shared with AI.
Inspect AI prompts, uploads and agent data exchanges; block sensitive information transfers based on configured data protection policies.
How It Works

From Hidden AI Usage to Enforced Governance

01
Discover public GenAI, SaaS copilots and employee-developed AI agents across the IT landscape
02
Link discovered AI usage to users, roles, devices and AI destinations
03
Define sanctioned AI services and agent permissions using identity-aware policies
04
Apply prompt and data protection controls and retain AI activity records for governance
Real-World Scenario

An employee builds an AI workflow

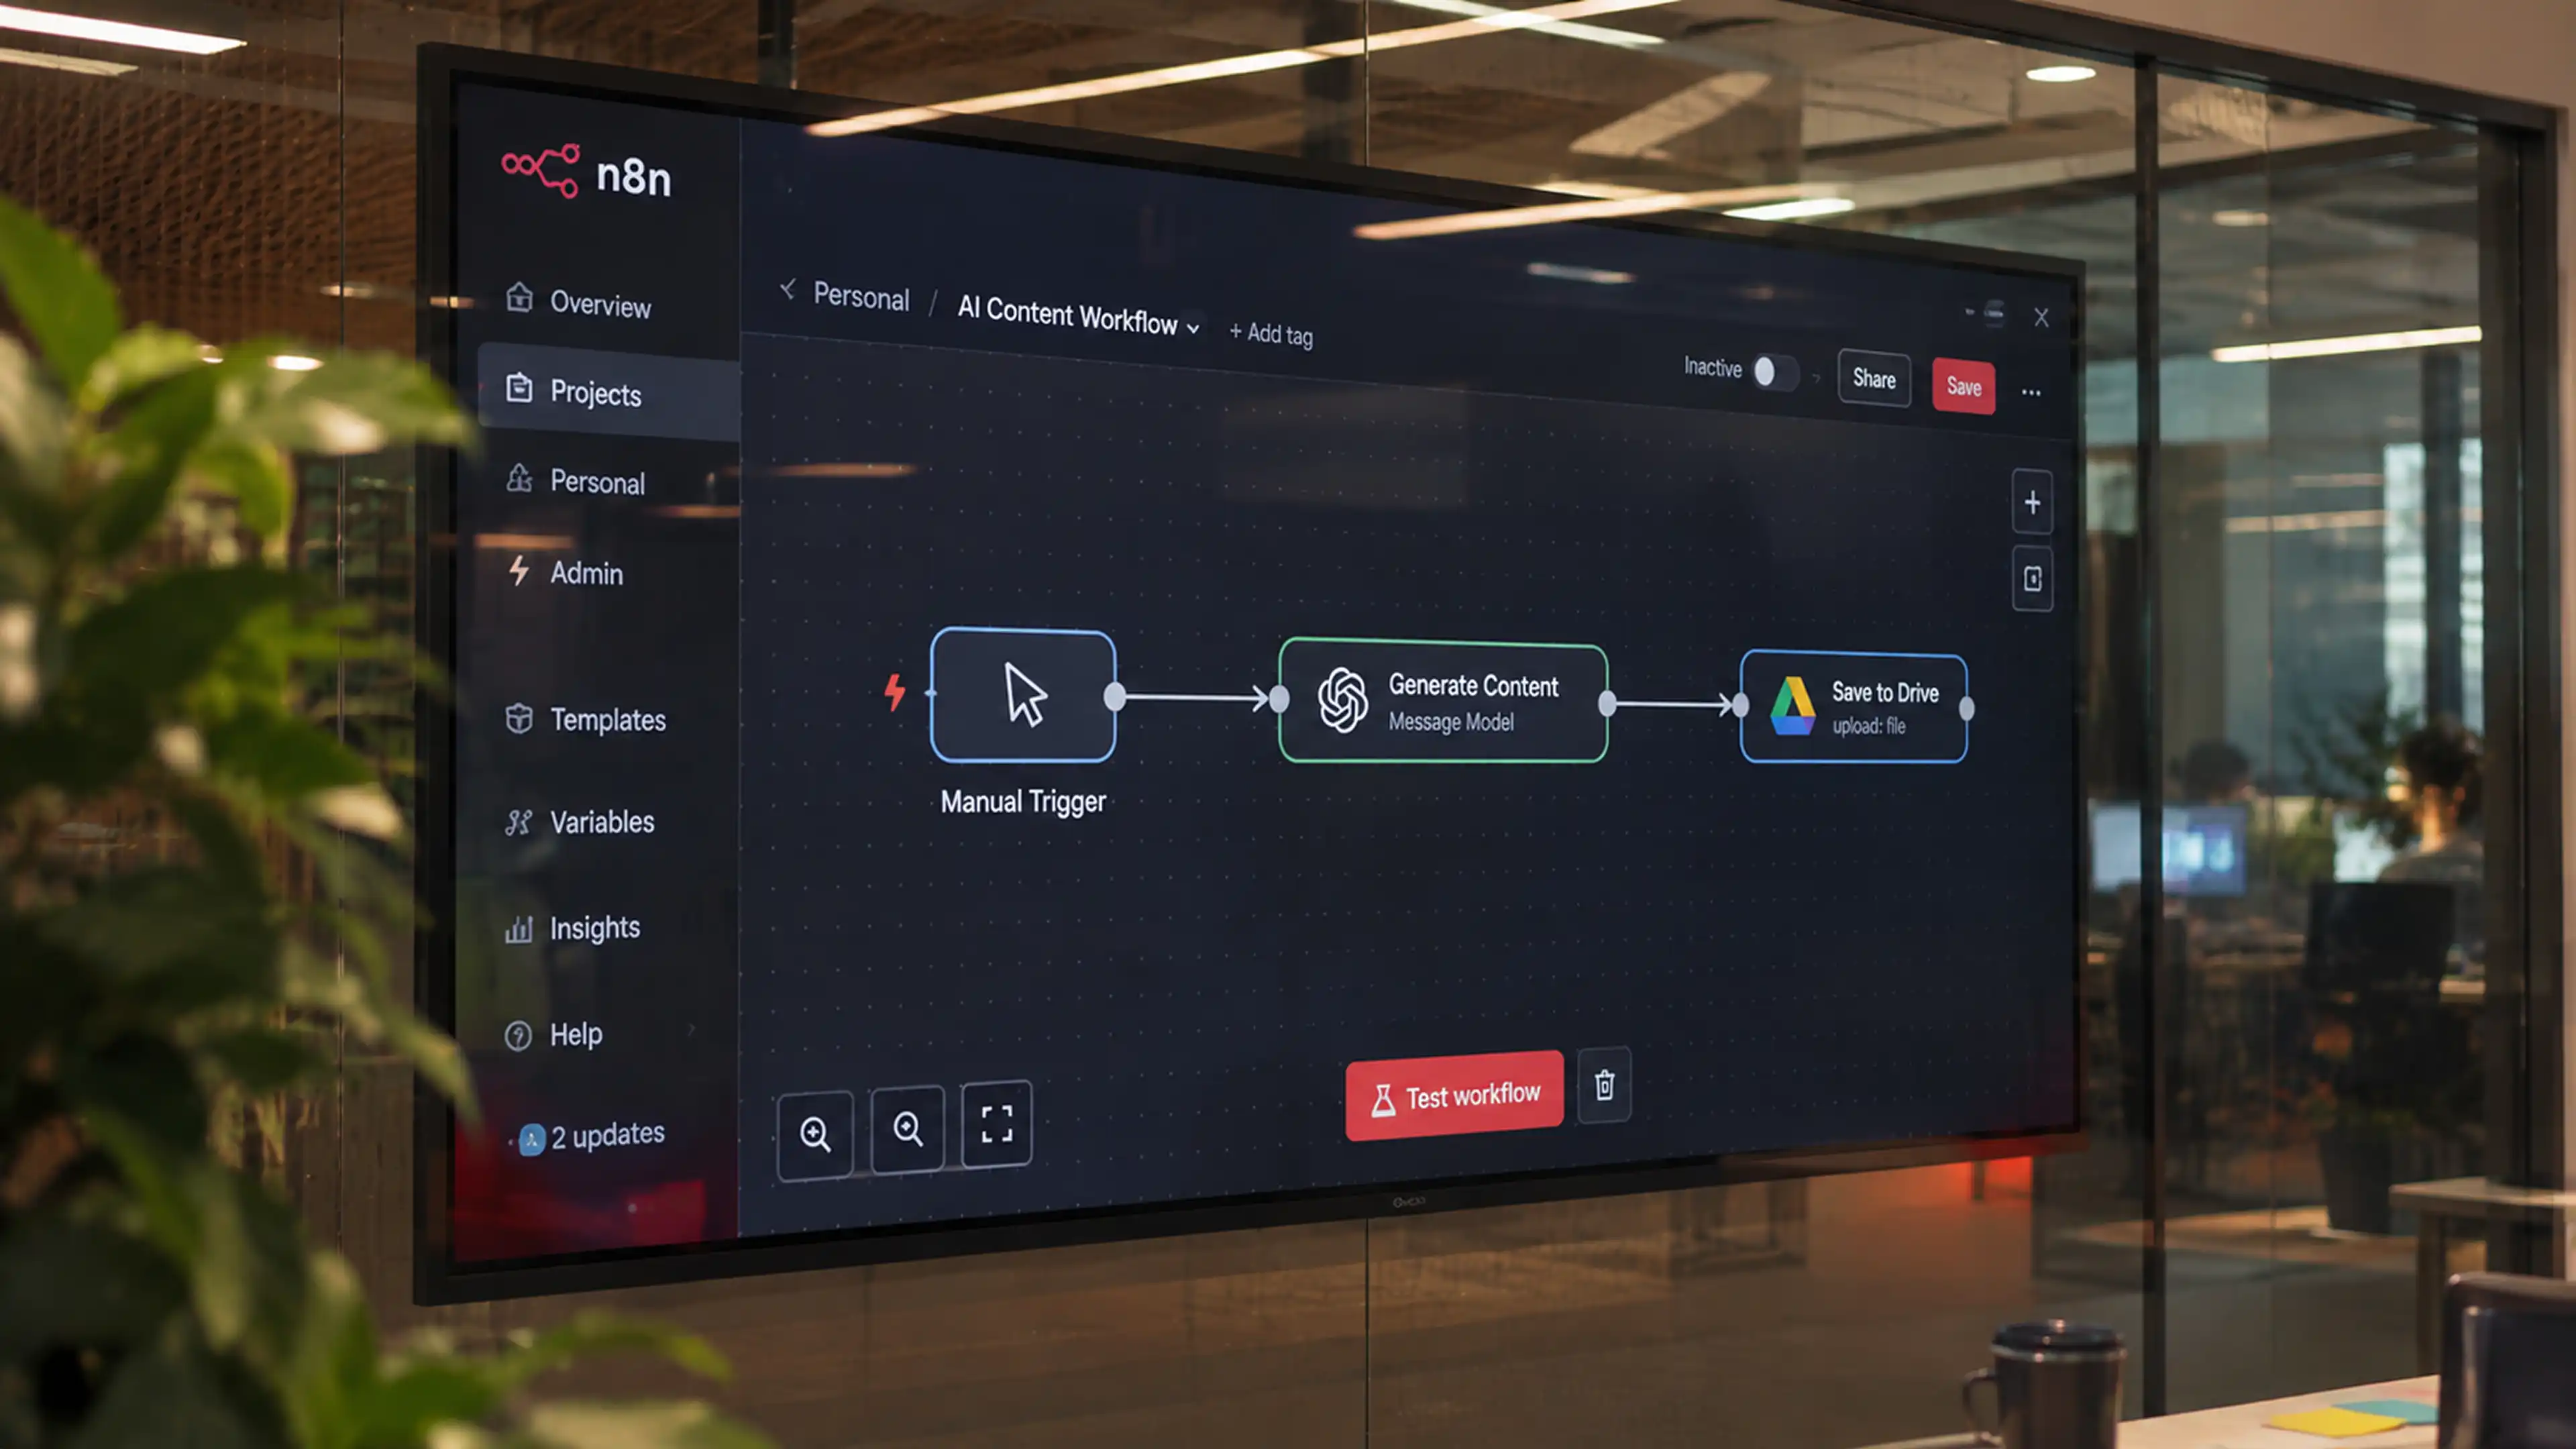
An employee creates an AI workflow using n8n and connects it to a business SaaS application. Zaperon makes the agent visible, attributes usage to the employee, and applies access and data protection rules to its interactions instead of leaving the workflow outside security oversight

01
Discover: Surface the employee-built AI workflow and its SaaS connections
02
Associate: Identify the employee, device and applications involved
03
Govern: Apply identity-aware authorization, DLP and activity monitoring
Business Outcomes

Bring Shadow AI Into View and Under Control

Enable secure BYOD access for assigned employees and contractors across desktops and mobile devices
Enforce application-by-application BYOD permission and desktop/mobile access policies
Reduce data exfiltration risk while isolating enterprise data from users’ personal information
What's New

Related Insights & Resources

Frequently Asked Questions

Still have a questions?
Can't find the answer to your question? Send us an email and we'll get back to you as soon as possible.

Request a Demo

How is Shadow AI different from Shadow IT?
Shadow AI focuses specifically on AI tools and agents, including their prompts, model interactions and access to enterprise data. Shadow IT is the broader category of unauthorized technology use.
Must every newly discovered AI tool be blocked?
No. Admins can allow approved applications and agents, restrict unapproved destinations, and apply identity-aware data protection policies appropriate to the user and workload.
What types of AI agents are covered by Shadow AI?
Zaperon discovers public GenAI services, SaaS copilots and self-developed agents created or launched by employees—including workflows built using Microsoft Copilot or automation platforms such as n8n. These are brought under identity-aware access, data protection and activity monitoring policies.

Take Control of Your
Security in the AI Era

Book a Demo