See Every AI Interaction. Enforce Policy in Real Time

Monitor GenAI, SaaS copilots, autonomous agents and self-hosted LLMs across MCP and A2A workflows; inspect prompts, tool activity and data with complete audit visibility
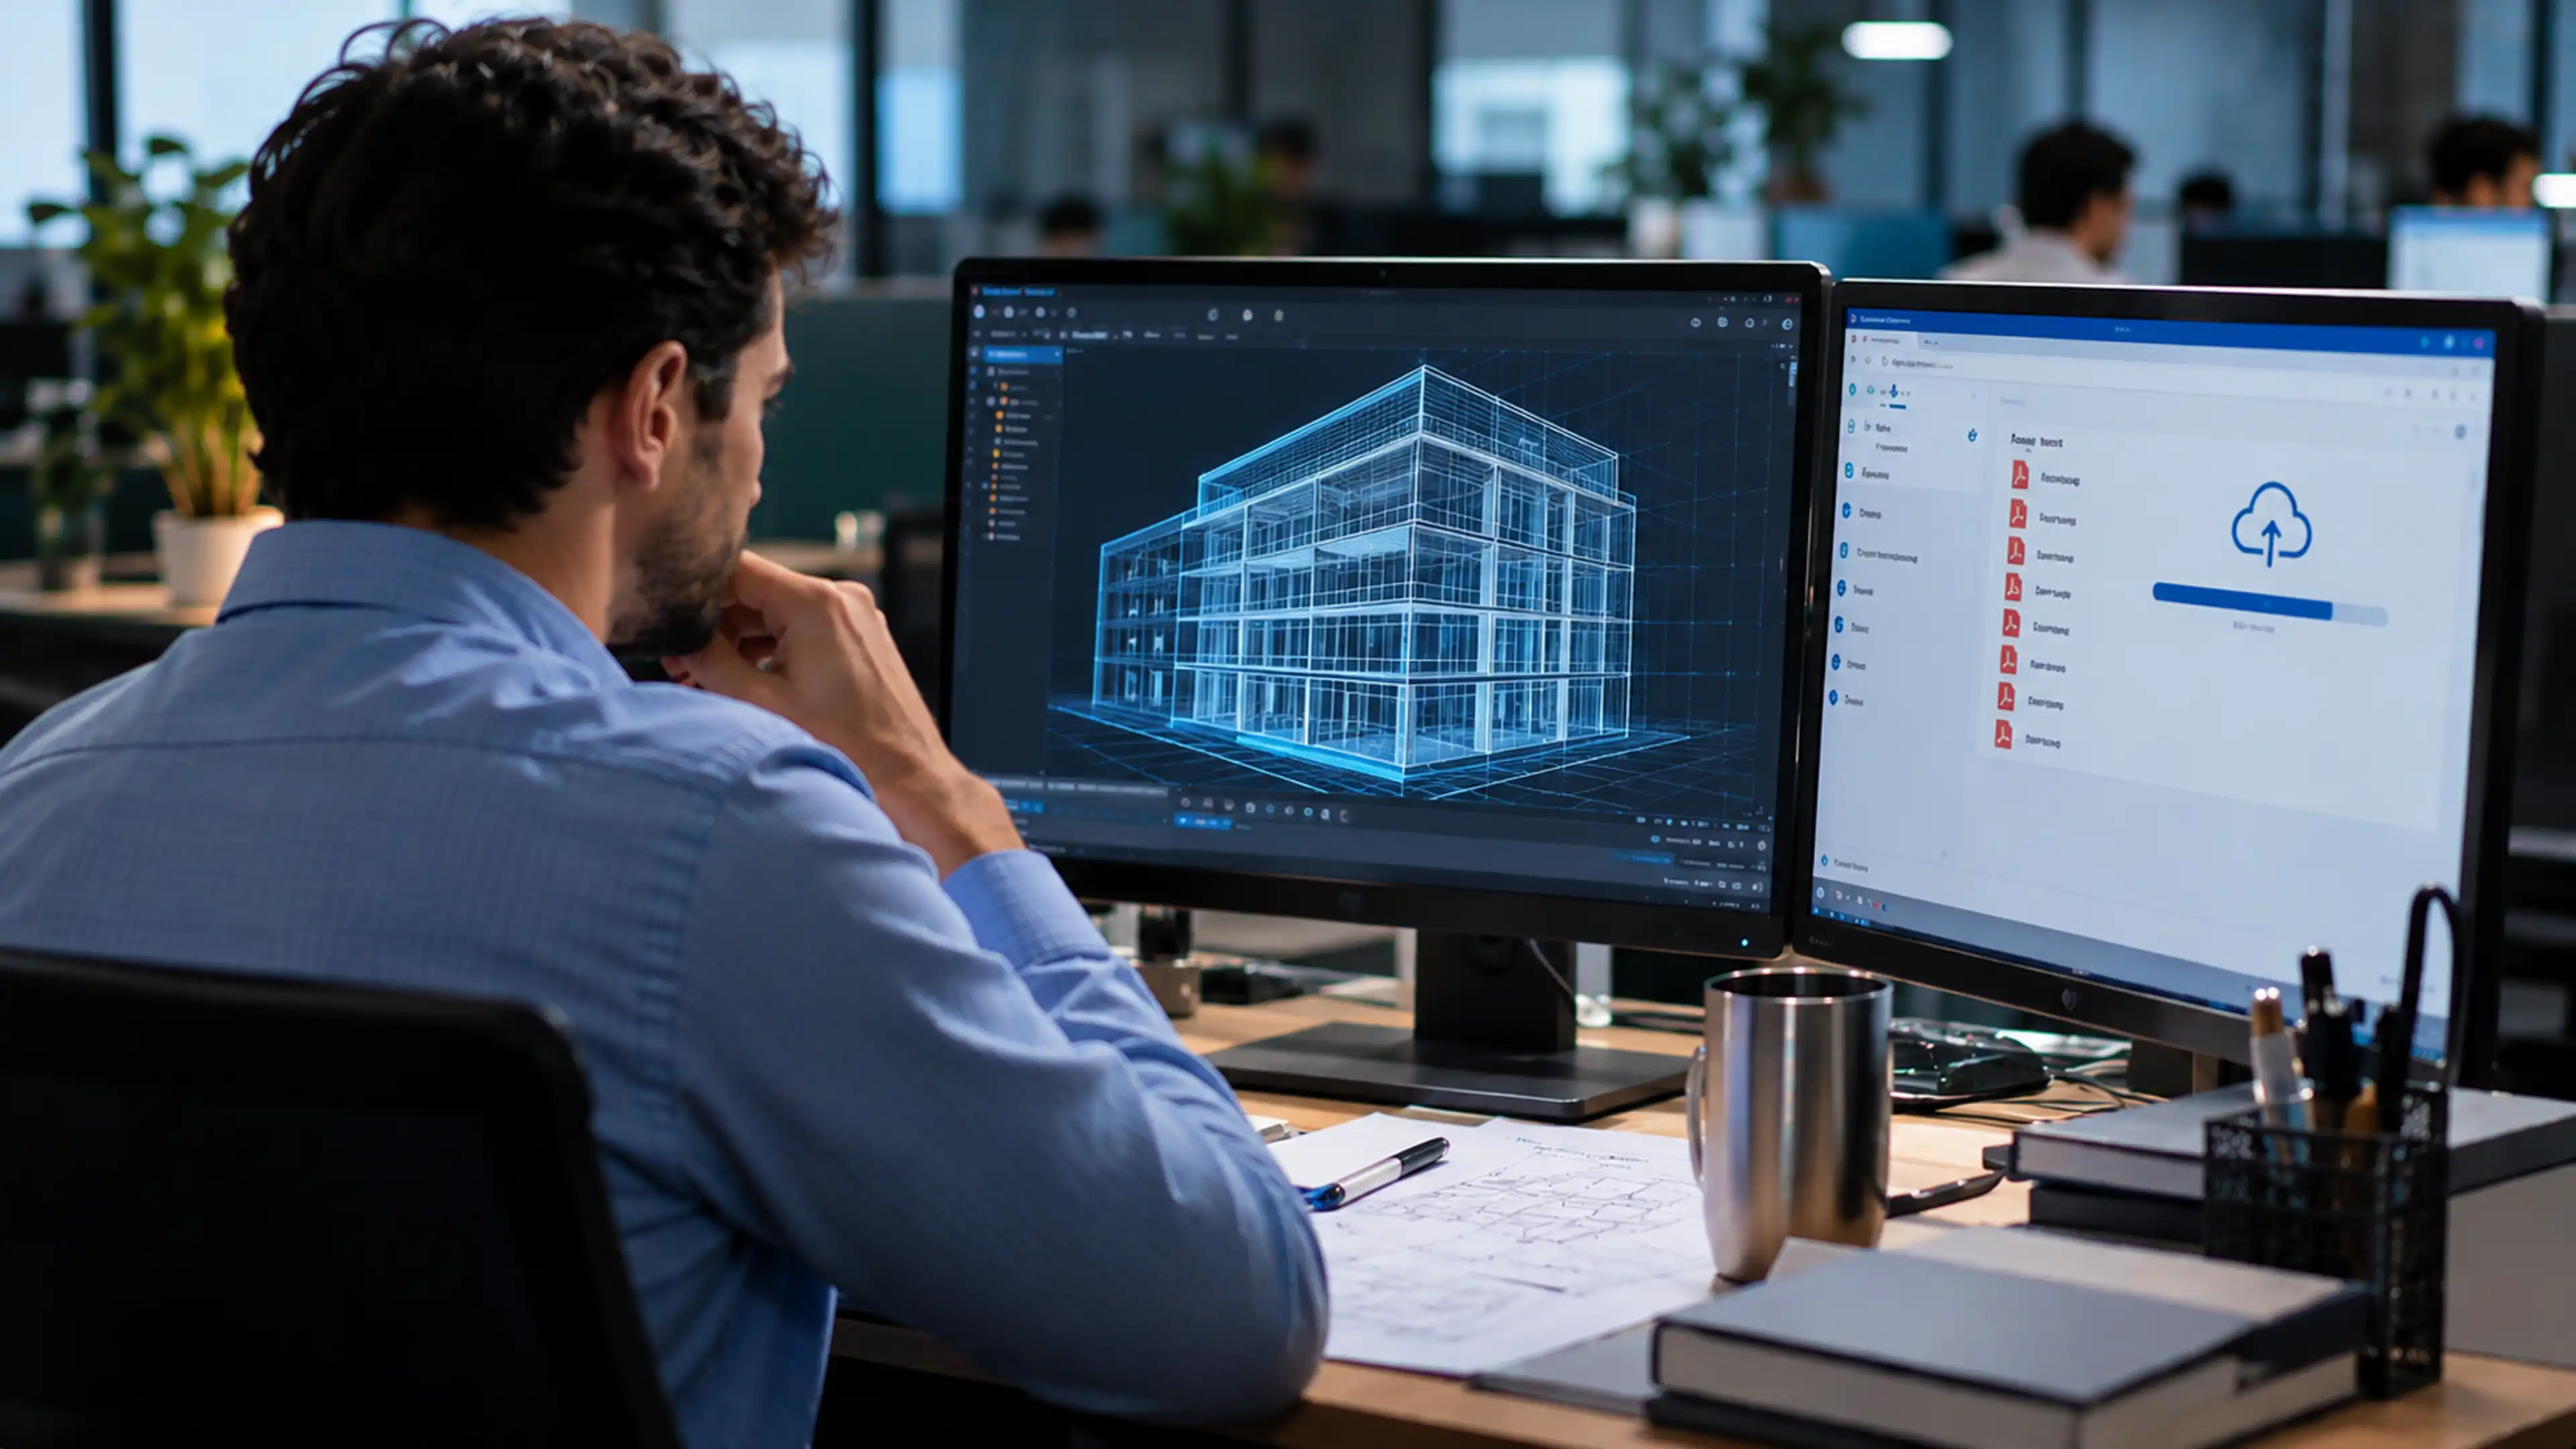
Monitoring and security policy enforcement for enterprise AI interactions
Challenges

AI traffic requires more than destination visibility

Seeing which AI service is used is only the first step. Sensitive information may be submitted in a prompt, a copilot may retrieve confidential records, or an autonomous agent may invoke an MCP tool or exchange data with another agent. Security teams need visibility into the interaction and the ability to enforce policy in real time
Unseen prompts
Security teams need visibility into sensitive content shared with AI
Tool-call exposure
Autonomous agents can invoke MCP tools and exchange data through A2A
Audit complexity
AI interaction events must be traceable for governance reviews
Capabilities

How Zaperon monitors AI interactions

Four connected security controls bring visibility, authorization, enforcement and auditability together.
Monitor AI interaction activity
Track AI prompts, data exchanges and agent interactions across GenAI, SaaS copilots, autonomous agents and self-hosted LLMs
Inspect prompts, MCP tools and data
Evaluate content and tool requests for security and sensitive-data risk, including MCP and A2A architectures
Enforce user-aware runtime policies
Apply authorization and data guardrails based on identity, role, device context, agent and requested action
Preserve complete audit visibility
Maintain AI interaction logs that link users and agents to prompts, tool activity, data exchange and policy decisions
How It Works

Inspect, Enforce and Audit AI Interactions

01
Identify relevant GenAI, SaaS copilot, autonomous-agent and self-hosted LLM interactions
02
Define permissions and content policies for prompts, MCP tool calls and data exchange
03
Enforce configured runtime allow/block decisions across AI interactions and A2A workflows
04
Review complete AI interaction audit logs for security investigations and governance
Real-World Scenario

An AI workflow handles confidential data

An employee directs an autonomous agent to summarize a customer dataset through a SaaS copilot and a self-hosted LLM. Zaperon monitors the prompt, MCP tool access and agent-to-agent data movement, prevents a prohibited disclosure and logs the interaction

01
Observe: Inspect prompts, agent calls and exchanged information
02
Enforce: Apply real-time interaction and data-protection policies
03
Audit: Record identity and policy context for every interaction
Business Outcomes

Make AI Activity Visible, Controlled and Auditable

Enable secure BYOD access for assigned employees and contractors across desktops and mobile devices
Enforce application-by-application BYOD permission and desktop/mobile access policies
Reduce data exfiltration risk while isolating enterprise data from users’ personal information
What's New

Related Insights & Resources

Frequently Asked Questions

Still have a questions?
Can't find the answer to your question? Send us an email and we'll get back to you as soon as possible.

Request a Demo

How is interaction monitoring different from Shadow AI discovery?
Shadow AI discovery identifies which AI tools and employee-built agents are being used. Interaction monitoring inspects the prompts, MCP tools, data exchanges and actions taking place inside those AI workflows.
Which AI interactions does Zaperon monitor?
Zaperon monitors AI interactions across GenAI, SaaS copilots, autonomous agents and self-hosted LLMs, including workflows using MCP tools and A2A agent architectures.

Take Control of Your
Security in the AI Era

Book a Demo